
Published: October 23, 2026
Category: Cybersecurity
Reading time: 5 minutes
Imagine opening your website one morning and finding it offline. Your customers cannot access your services. Unfamiliar files appear on your server. Or worse, your business data may have been exposed.
What if the problem isn't your website's code, but the software running underneath it?
On October 21, 2026, the PHP development team released emergency security updates for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, commonly referred to together as PHP2Shell. Both received a critical severity score of 9.2 out of 10. Under certain conditions, they can allow attackers to execute malicious code on vulnerable servers without logging in.
The important question isn't whether your website looks normal today. It's whether the software powering it is secure.
What exactly is the PHP2Shell vulnerability?
PHP is the server-side technology behind millions of websites, content management systems, and web applications. It processes requests, handles files, interacts with databases, and powers the features visitors use every day.
The PHP2Shell vulnerabilities involve problems in how the PHP runtime manages memory during request processing.
In simple terms, certain error-handling scenarios can leave PHP in an unsafe internal state. An attacker may be able to exploit these flaws to execute code on a vulnerable server, potentially gaining access to resources available to the PHP process.
The two vulnerabilities have different technical causes:
CVE-2026-109618: Involves memory corruption during out-of-memory error handling.
CVE-2026-109619: Involves stale internal state that can remain after memory has been freed.
What makes these vulnerabilities especially concerning is that exploitation may occur before your application's own code gets a chance to run. Updating your website's plugins or fixing a bug in your application does not, by itself, resolve a vulnerable PHP runtime.
Why should website owners pay attention?
You might be thinking, "My website is working perfectly. Why should I worry?"
That is exactly why vulnerabilities can go unnoticed. A website may continue to operate normally even when its underlying software needs an urgent security update.
Consider these scenarios:
Business websites: A compromised server could disrupt your online presence and affect customer trust.
WordPress websites: Your themes and plugins might be up to date while the PHP runtime remains vulnerable.
E-commerce stores: A server compromise could threaten sensitive business operations and customer information.
Legacy applications: Older PHP installations may no longer receive standard security updates from the PHP project.
These are potential consequences, not proof that every affected website has been compromised. Actual risk depends on the version, configuration, exposure, and available privileges.
The lesson is simple: protecting your website means protecting the entire technology stack, not just the visible application.
Which PHP versions are affected?
According to the published security advisories, the affected versions include PHP releases before the following patched versions:
PHP branch | Fixed release |
|---|---|
PHP 8.5 | 8.5.12 |
PHP 8.4 | 8.4.27 |
PHP 8.3 | 8.3.36 |
PHP 8.2 | 8.2.35 |
These are the fixed releases announced for the respective branches. Use an appropriate later security release where available.
What if your website uses PHP 8.1 or older?
These branches have reached end of life under the PHP project's normal support policy. Some operating-system vendors and long-term-support providers offer backported security patches, so confirm your vendor's position rather than assuming that an old version is either fixed or unfixable.
PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP, and LiteSpeed deployments also need attention. The PHP security team identifies Apache mod_php as a particularly high-risk configuration.
Remember that the PHP version on your laptop may differ from the one serving your live website.
How to protect your website
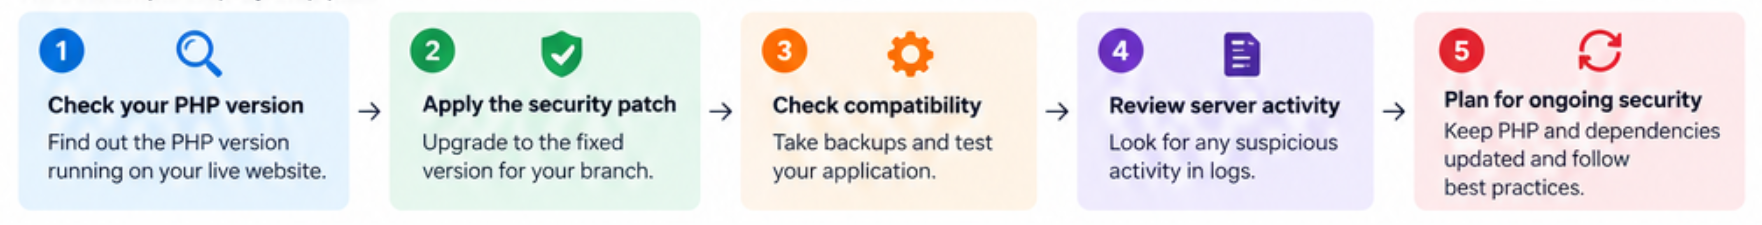
You do not need to panic, but you should take this seriously. Here is a practical response plan.
1. Check your production PHP version
Identify the PHP runtime actually used by your live website. If you use managed hosting, a control panel, containers, or a cloud platform, verify the version serving the production application.
2. Apply the relevant security patch
Upgrade to an appropriate fixed PHP release. If your hosting provider manages PHP, contact its support team and ask whether the affected runtime has been updated.
Updating WordPress, a theme, or a plugin does not automatically update PHP itself.
3. Check application compatibility
Before upgrading, review compatibility with the target PHP release. Take verified backups, test critical functionality, and plan a controlled deployment.
4. Review suspicious activity
Patching fixes the known vulnerabilities, but it does not establish that a server was never compromised.
Review relevant web-server, application, authentication, and system logs. Investigate unfamiliar files, unexpected processes, new accounts, or unusual outbound connections.
If you suspect an attack, preserve evidence and investigate before treating the update as a complete recovery.
5. Build a routine for future updates
Keep PHP and its dependencies supported and patched. Maintain reliable backups, use least-privilege permissions, restrict unnecessary access, and establish a process for responding to security advisories.
Patching is the primary fix. Temporary mitigations can reduce exposure in some situations, but they should not be treated as a substitute for installing the appropriate security update.
What if you don't know how to patch your server?
Many small businesses, freelancers, and website owners rely on hosting providers or developers to manage their infrastructure. Others maintain their own websites but lack the time or experience to investigate a critical server-side vulnerability.
The first step is to identify your PHP version and confirm whether the relevant security update has been applied.
You don't need to figure everything out alone.
Need help securing your PHP website? I'll help for FREE.
I'm Mohammed Musab Khan, and I want to help website owners take practical steps to protect their online businesses.
I'm offering FREE assistance with checking exposure to these PHP vulnerabilities and applying the relevant security patches, where the hosting setup and access arrangements permit.
Here's how to get started:
Contact me and explain that you need help with the PHP security update.
Share your website URL and, if known, your PHP version or hosting setup.
I'll help you understand what needs attention and the next steps for applying the appropriate patch safely.
You do not need to share passwords or private server credentials over chat.
Let's protect the work you've built.
Mohammed Musab Khan
Phone: +91 9167478301
Website: uzaif.com
The best time to check your website's security is before a vulnerability becomes an incident. Get in touch for free PHP security patch assistance.
Offer scope: Free assistance with checking exposure and applying relevant PHP security patches, subject to hosting access and technical feasibility. Additional remediation, hosting fees, or broader security work will be discussed separately before proceeding.
Official resources
PHP security announcements
CERT-EU advisory on critical PHP vulnerabilities
Google Cloud technical analysis
This article is for general security awareness and does not replace a review of your specific server environment.
Discussion (0)